test import

Categories

Ad Home

Responsive Ads Here

Labels

642-813 SWITCH (2) 642-902 ROUTE (2) 643-832 TSHOOT (1) Access Based Enumeration (1) access list (2) AIX (1) Anti Malware (16) AutoIT (1) backtrack (4) Basic Networking (3) Blogspot (2) bootable USB (1) can not download attach file from gmail (1) ccna (9) CCNA Lab (19) centos (3) Check (1) Check_MK (3) cisco (51) Dell (1) DHCP (1) Download (2) Dynamic Host Configuration Protocol (1) ebook (2) Ebooks (18) eigrp (1) encapsulation (3) esxi5 (2) exam (13) exchange server 2010 (3) facebook (2) firewall-cmd (1) firewall-config (1) firewalld (1) Frame Relay (4) Free Router Simulator Softwares (1) FreeNAS (1) GhostSurf (1) gns3 (1) Hacking Security (5) hardware (1) hotspot (1) How to Change Windows 2008 R2 SID (1) How to create VPN network on Linux (1) How to install openSSH on AIX 5.3 (1) How to Install the Microsoft Core Fonts on Fedora 19 (1) HP (1) IBM (1) Infrastructure Monitoring (3) InterVLAN (1) ip routing (3) IPSec (2) ipv6 (1) IT (122) joomla (1) Kiến thức (278) LAN Technology (3) life skills for (1) lifeskills (2) linux (13) Linux-Unix (24) mac address (1) Magazine (9) Mail (2) mail server (1) MCSA (7) Microsoft (28) mikrotik (3) Multipoint (1) Nagios (3) NAT (1) nested (1) Network (1) Network Load Balancing (1) News (1) Nghệ thuật sống (1) O365 (4) Office 365 (4) OSPF (1) Packet tracer (19) Pass4sure (1) Point to Point (1) Point-to-Point Protocol (PPP) – CHAP (1) Point-to-Point Protocol (PPP) – PAP (1) Policy (3) Port Security (1) Practice Labs (19) Prerequisites (1) proxy (1) relax (7) rhel7 (1) RIP (1) routerOS (3) Routing (1) SAN (1) SAN Storage (1) Scripts (6) Server (1) server room (1) Sharepoint Server 2007 (1) Sharepoint Server 2010 (1) Spanning Tree Protocol (1) SSH login without password (1) Static Default Route (1) Storage (1) subnet (1) switch (1) System Requirements for Windows Server 2012 (1) Tản mạn (2) tcp-ip (1) telnet (1) TestInside (1) Thư giãn (4) Thủ thuật (2) tip (3) Tips + Tricks (29) trick (1) Tutorial (29) Tutorialvirtual server HighAvailability (1) ubuntu (4) unix (3) Unix-Linux (8) usb (1) Virtual Private Network (VPN) - IPsec (Site-to-Site) (1) Virtual Trunking Protocol (1) Virtualization (2) Virtualization HighAvailability (1) virus (5) vmware (6) vpn (4) vpn client (1) vpn client to site (2) vpn site to site (2) vSphere 5 (6) vSphere 5.1 (1) WAN Technology (13) Warranty (1) wildcard mask (1) windows 7 (1) windows 8 (1) windows server 2008 (3) Windows Server 8 (1)

Facebook

Ethereum

Subscribe for New Post Notifications

Ripple

Ethereum Price

Monday Tuesday Wednesday
$402.89 $384.06 $396.34

Contact Form

Name

Email *

Message *

Bitcoin

Litecoin

Browsing Category " vpn site to site "

VPN SITE TO SITE (router cisco)

VPN SITE TO SITE (router cisco)
On ccna
Cấu hình VPN Site to Site trên router Cisco ( cli )

1.Topology


2.Yên cầu 

Cấu hình VPN cho phép 2 LAN ở router HQ và router Branch liên lạc được với nhau.
3.Cấu hình: 


a. Cấu hình  cơ bản trên các router 

-Router ISP: chỉ cấu hình hostname và IP của các interface như mô hình trên
- Router HQ: cấu hình hostname và ip theo mô hình, sau đó cấu hình default route. 

HQ(config)#ip route 0.0.0.0 0.0.0.0 113.114.115.2 

- Router Branch: cấu hình hostname và ip theo mô hình, sau đó cấu hình default route. 

Branch(config)#ip route 0.0.0.0 0.0.0.0 115.114.113.2

 b.Cấu hình VPN theo các bước sau:

Trên router HQ 

Bước1: Tạo Internet Key Exchange (IKE) key policy.

HQ(config)#crypto isakmp policy 9

HQ(config-isakmp)#hash md5

HQ(config-isakmp)#authentication pre-share

Bước 2: Tạo shared key để sử dụng cho kết nối VPN

HQ(config)#crypto isakmp key VPNKEY address 115.114.113.1    (ip của router branch)


Bước3: Quy định lifetime 

HQ(config)#crypto ipsec security-association lifetime seconds 86400

Bước4: Cấu hình ACL dãy IP có thể VPN.

HQ(config)#access-list 100 permit ip 192.168.1.0 0.0.0.255 192.168.2.0 0.0.0.255

Bước 5:  Define the transformations set that will be used for this VPN connection

HQ(config)#crypto ipsec transform-set SETNAME esp-3des esp-md5-hmac


Bước6:  Tạo cypto-map cho các transform, setname

HQ(config)#crypto map MAPNAME 10 ipsec-isakmp

HQ(config-crypto-map)#set peer 115.114.113.1   (ip của router branch)

HQ(config-crypto-map)#set transform-set SETNAME  ( setname ở bước 5)

HQ(config-crypto-map)#match address 100  (100 : acl-number ở bước 4 )

Bước7: Gán vào interface

HQ(config)#inter s0/0/0
HQ(config-if)#crypto map MAPNAME  (mapname ở bước 6)

Trên router Branch


Thực hiện tương tự theo 7 bước như trên router HQ.
Có một số thay đổi nho nhỏ ở các bước sau:
- bước 2:
Branch(config)#crypto isakmp key VPNKEY address 113.114.115.1 (ip của router HQ)

- bước 4:
Branch(config)#access-list 100 permit ip 192.168.2.0 0.0.0.255 192.168.1.0 0.0.0.255

- bước 6:
 Branch(config-crypto-map)#set peer 113.114.115.1   (ip của router HQ)


Phần trên các router cấu hình đến đây đã xong!

Kết quả: ping từ LAN 192.168.1.0/24 sang LAN 192.168.2.0 /24 đã thành công!


---------------

Một số lệnh kiểm tra cấu hình vpn


show crypto isakmp sa

show crypto ipsec sa

show crypto engine connections active

and show crypto map

-----------

Mô hình tôi làm trên packer tracer 5.3 + config files : download

CHÚC CÁC BẠN THỰC HIỆN THÀNH CÔNG! 

Copyright by http://www.lecuong.info
THIẾT LẬP MÔ HÌNH VPN (Gateway – Gateway)

On IT

Virtual Private Network (VPN) - Mạng riêng ảo là một công nghệ cho phép mở rộng phạm vi của các mạng LAN (Local Area Networks) mà không cần bất kì đường dây riêng nào.VPN được dùng để kết nối các chi nhánh phân tán về mặt địa lí thành một mạng duy nhất và cho phép sử dụng từ xa các chương trình ứng dụng dựa trên các dịch vụ trong công ty.

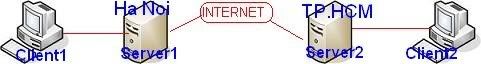
- Mô hình bài Lab như sau:

Highslide JS

Chúng ta có 4 máy :
    + Client1 , Server1 đặt tại Hà Nội
    +Client2, Server2 đặt tại Tp.HCM
Quy ước:
+Card Lan: nối giữa các máy trong nội bộ với nhau
+Card INTERNET: nối vào SW để ra internet
- Đặt địa chỉ IP cho các máy như sau:

Client1 : có 1 card mạng

Card LAN:

IP Address : 172.16.1.2

Subnet Mask : 255.255.255.0

Default Gateway : 172.16.1.1

Preferred DNS : để trống

SEVER1: sử dụng 2 card mạng

Card INTERNET:

IP Address : 192.168.1.1

Subnet Mask : 255.255.255.0

Default Gateway : 192.168.1.254

Preferred DNS : 210.245.24.20

Card LAN:

IP Address : 172.16.1.1

Subnet Mask : 255.255.255.0

Default Gateway : để trống

Preferred DNS : để trống

SERVER2:
Card INTERNET :

IP Address : 192.168.2.1

Subnet Mask : 255.255.255.0
Default Gateway : 192.168.2.200
Preferred DNS : 210.245.24.22

Card LAN :
IP Address : 172.16.2.1

Subnet Mask : 255.255.255.0

Default Gateway : để trống
Preferred DNS : để trống


Client2:

Card LAN:

IP Address : 172.16.2.2

Subnet Mask : 255.255.255.0

Default Gateway : 172.16.2.1

Preferred DNS : để trống

-------------------------------------------------------------------------------
Các bước chuẩn bị đã xong, chúng ta bắt đầu thực hiện bài LAB nhé!

I• Cấu hình VPN trên máy server1

- B1: Tạo user account
User name: hanoi
Password: hanoi
Cho phép user hanoi có quyền Allow Access

Highslide JS
- B2: Mở Administrative Tools -> Routing and Remote Access, click chuột phải trên SERVER1 chọn  Configuring and Enable Routing and Remote Access

Highslide JS
- B3:  Cửa sổ Welcome to the Routing and Remote Access Server Setup Wizard--Next--cửa sổ Configuration ---> check vào ô Custom Configuration và Next:

Highslide JS
- B4:  Cửa sổ Custom Configuration và check vào các ô: VPN access, Demand-dial connections (user for branch office routing) và LAN routing --> Next--> Finish ---> Yes

Highslide JS
- B5: Cửa sổ Routing and Remote Access -- click chuột phải trên Network Interface --> chọn New Demand-dial Interface

Highslide JS
- B6:  Cửa sổ Welcome ,click Next ->cửa sổ Interface Name và nhập vào hanoi ---> Next
***lưu ý: Interface name bên này là username bên kia ! ( hồi đi học cũng hay lẫn lộn cái vụ này ! hehe...)

Highslide JS
- B7:  Cửa sổ Connection Type--- chọn Connect using virtual private networking (VPN) --> Next

Highslide JS
- B8:  Cửa sổ VPN Type, chọn Point to Point Tunneling (PPTP) ---> Next

Highslide JS

- B9:  Cửa sổ Destination Address và nhập vào Host name đã đăng ký hoặc gõ vào IP tĩnh (nếu có) ---> Next

Highslide JS
- B10:  Cửa sổ Protocols and Security để mặc định ---> Next

- B11:  Cửa sổ Static Routes for Remote Networks ---> Add


Highslide JS

- B12:  Cửa sổ Static Route và nhập các giá trị như hình -- OK --- Next

Highslide JS

- B13:  Cửa sổ Dial Out Credentials, nhập các thông tin như sau:

• User name : saigon

• Domain : để trống

• Password : saigon

• Confirm password : saigon

và chọn Next --- Finish

Highslide JS

- B14:  Routing and Remote Access ---> click chuột phải trên  SERVER1 -- chọn Properties -- qua tab IP --> chọn Static address pool và Add

Highslide JS
- B15:  Cửa sổ New Address Range và nhập các giá trị như hình vẽ --> OK và chọn OK

Highslide JS

- B16:  Cửa sổ Routing and Remote Access và click chuột phải trên SERVER1 --- All Tasks ---> Restart

Highslide JS

II•Cấu hình VPN trên máy SERVER2

- Lặp lại các bước của phần Cấu hình VPN trên máy SERVER1 cho máy SERVER2, thay đổi các thông tin sau:


- Tại bước 1:

User name : saigon

Password : saigon
Cho phép user saigon có quyền Allow Access

- Tại bước 6 ( khai báo Interface )

Interface name: saigon

- Tại bước 12 (tạo Static Routes ) :

Interface : saigon

Destination : 172.16.1.0

Network mask : 255.255.255.0

Metric : 1

- Tại bước 13 (khai báo Dial Out Credentials ) :

User name : hanoi

Domain : (để trống)

Password : hanoi

Confirm password : hanoi


- Tại bước 14
 ( tạo Static Address Pool ):

Start IP Address : 172.16.2.200

End IP Address : 172.16.2.220


Đến đây mọi việc đã hoàn tất, hiện giờ 2 site Hà Nội và TP.HCM có thể truy xuất dữ liệu lẫn nhau được rồi đấy!
Chúc các bạn thực hiện thành công!!:)


Copyright by http://www.lecuong.info